Compliance you can show, not just claim
Guest Wi-Fi marketing under UK GDPR and PECR.
Most guest Wi-Fi tools give you a tick box. WiFinger gives you a ledger that cannot be edited, the exact wording each guest saw, and a consent evidence PDF you can show a regulator. Built to follow ICO guidance (our assessment, not a certification); not legal advice.
Wi-Fi marketing consent, done properly
Consent is never a condition of Wi-Fi
The marketing box is separate, optional and always unticked. The portal will not save a configuration that pre-ticks or requires it. Wi-Fi is granted whatever the guest chooses.
Explicit consent, not soft opt-in
Guest Wi-Fi sign-up is not a sale, so PECR’s soft opt-in does not apply. WiFinger relies on explicit consent only, per channel (email and SMS separately).
Wording names your organisation
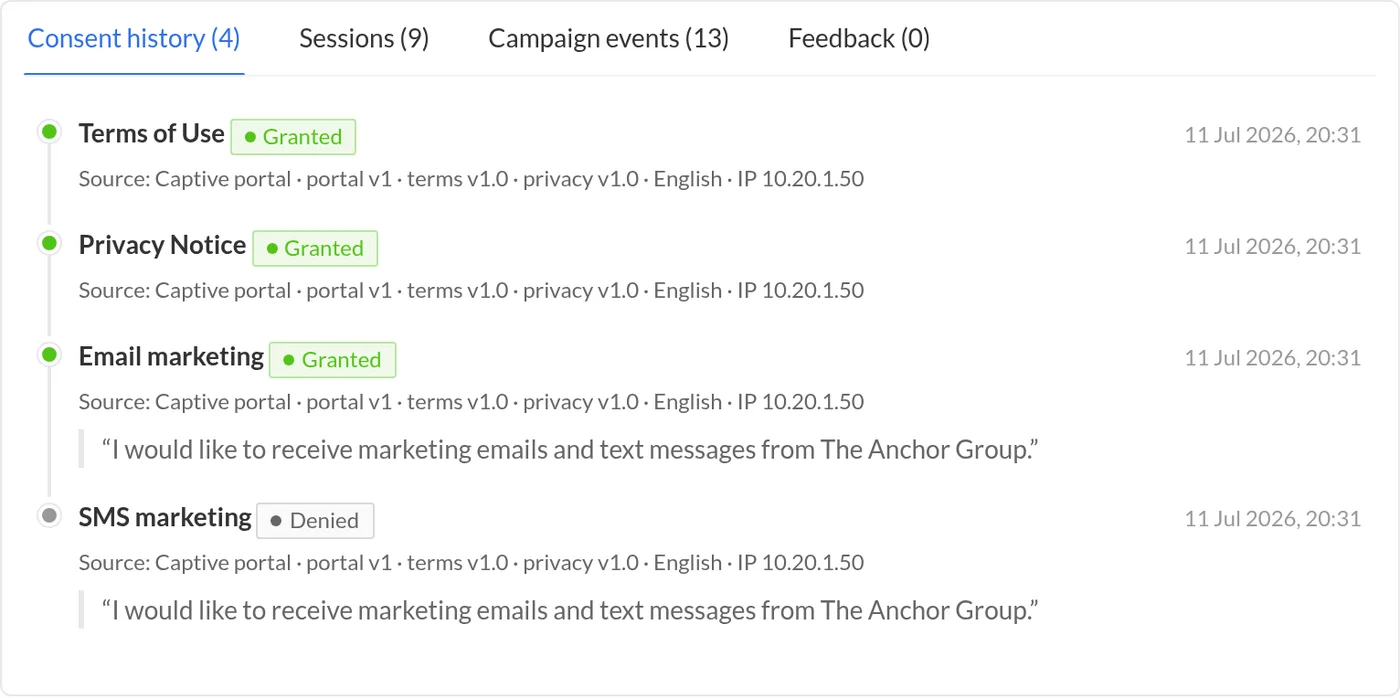
Consent text must include your venue name and is stored exactly as shown, with the privacy and terms version the guest saw.
Every message has a way out
Unsubscribe link and preference centre in every email and SMS, plus RFC 8058 one-click List-Unsubscribe. Withdrawal is recorded with its source and cancels in-flight automations.
Checked at send time, every time
Campaigns and automations check eligibility for each recipient at the moment of sending. Ineligible guests are logged as skipped, never sent.
Unticked is not withdrawal
A guest who signs in again without ticking records a "denied" row for that visit; an earlier opt-in stays valid until they withdraw it.
What you see, and what you don’t
Guests type their details to get online; that does not make them marketing contacts. What your team can see or export follows the guest’s current consent, live: a withdrawal hides the details at once, a new opt-in shows them at once. Hidden means hidden, not half-masked.
| Guest’s marketing consent | Mobile | Name, postcode, custom fields | |
|---|---|---|---|
| No marketing consent (not asked, declined or withdrawn) | Hidden | Hidden | Hidden (shown as “Guest”) |
| Email marketing only | Shown | Hidden | Shown |
| SMS marketing only | Hidden | Shown | Shown |
| Email and SMS marketing | Shown | Shown | Shown |
Applies to guest lists and search, Customer 360, exports, sessions, the consent list, campaign reports, webhooks and CRM sync. The consent evidence itself is kept, because it is your proof.
The consent ledger
Each consent event stores the guest, site and session, a UTC timestamp, IP address and device, the consent type and channel, the exact wording, the privacy and terms version, the portal version, the source, and the status. Withdrawals add their own timestamp and source.
Nobody can edit it. Not an admin, not our support team, not a bug. The rule lives in the database, and the audit log records every export.
Controls built in
Append-only ledger
A database trigger rejects any change to recorded consent facts. Only granted-to-withdrawn transitions, erasure minimisation and merges are allowed.
Evidence PDF
One click on a guest record produces a printable evidence document: every consent row, exact wording, versions, withdrawal, integrity statement and who generated it.
Retention schedules
Session metadata 13 months by default; inactive guests erased after 24 months; consent evidence kept 6 years. All configurable per organisation and enforced hourly.
Rights requests
Export (JSON) and erasure requests are tracked with a 30-day SLA. Erasure keeps a hashed suppression entry so the person is never re-marketed.
UK hosting
The service and its database are hosted in the UK (London). WiFinger is your processor under a Data Processing Agreement; sub-processors (hosting, email, SMS, payments, AI) are listed in it, with the safeguards used for any transfer outside the UK.
MFA & roles
TOTP two-factor login with recovery codes. Organisations can require it for admins or everyone; WiFinger staff must use it.
Audit log
Every change, export, login and "open as customer" by our support team is written to an append-only audit log you can read.
Data minimisation
Guests who don’t opt in are never shown to you with their email or phone. No inspection of guest traffic. MAC addresses stored as hashes; the reversible copy needed for the session is encrypted and deleted when it ends. Wi-Fi passwords are never stored.
Want the detail? Read the Data Processing Agreement and the sub-processor list, or ask for the compliance pack (retention defaults, security summary) via the contact form. WiFinger is operated by CLI Secure Ltd (company no. 10813832), registered with the ICO under ZC139349.
Common questions about guest Wi-Fi and GDPR
Is guest Wi-Fi data collection legal in the UK?
Can I see the email of a guest who did not opt in?
Who is the data controller?
Do I still need my own privacy notice?
What about footfall analytics and cookies?
See the ledger with your own data.
14 days free, no card. Or book a demo and we will walk through the evidence PDF.